01
Incoming Email
Analyze, score, quarantine recommend, review
Defensive email-security automation that analyzes suspicious messages, scores risk, and supports analyst review workflows.
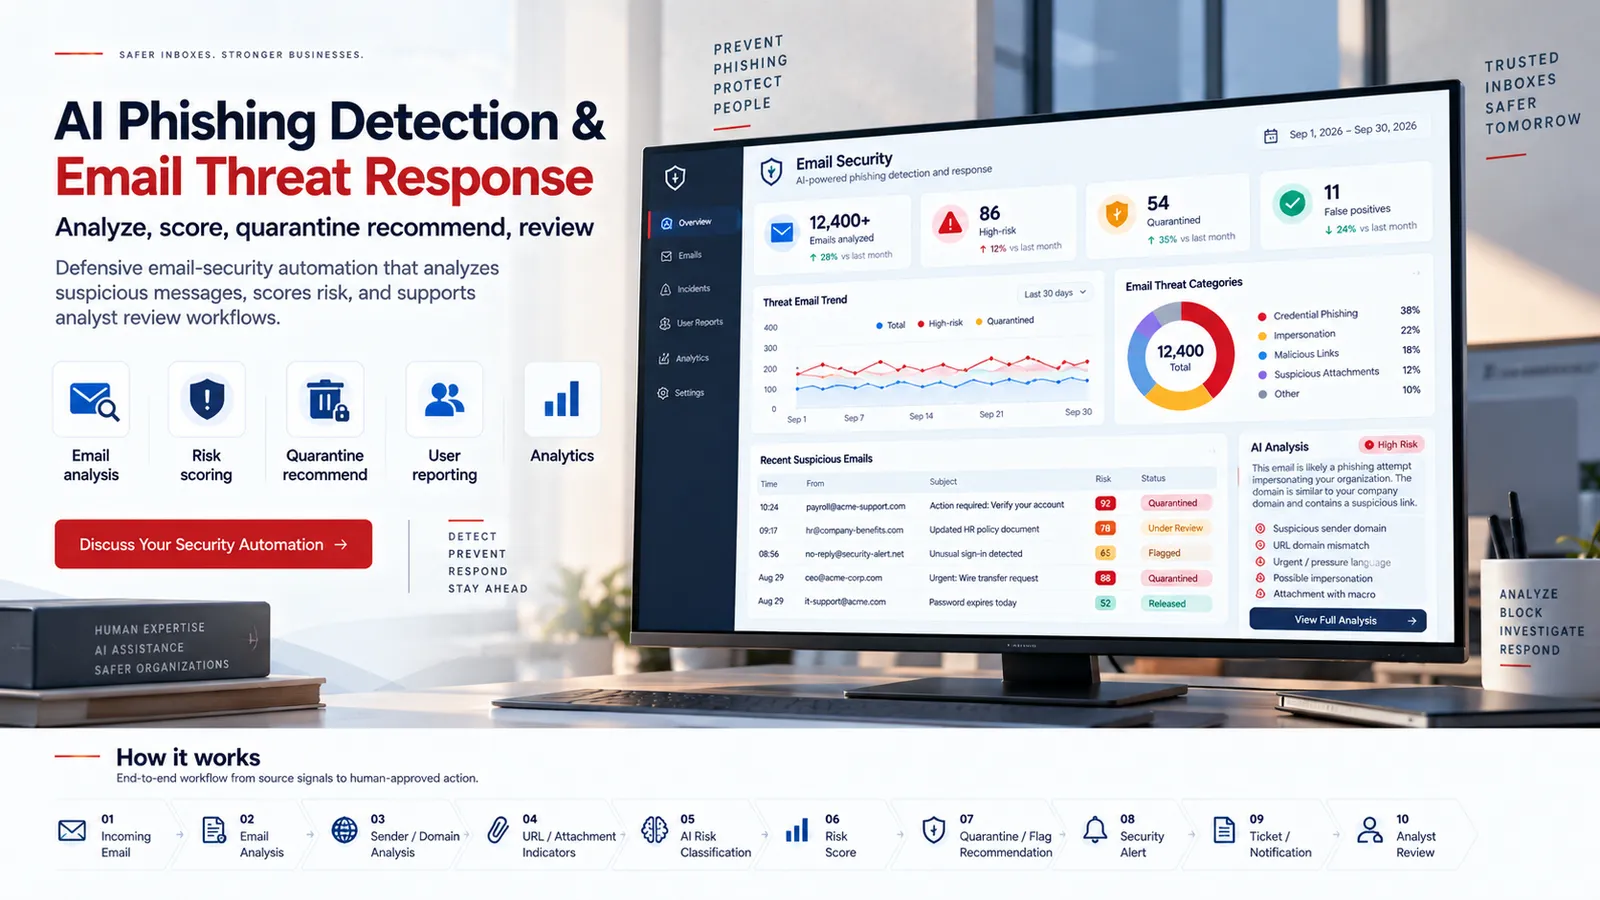
12,400+
Emails analyzed
86
High-risk
54
Quarantined
11
False positives
Employees report suspicious emails inconsistently. Security teams lack a structured way to analyze indicators, score risk, quarantine candidates, and document analyst decisions.
A defensive email threat response workspace that analyzes sender/domain/URL/attachment indicators, applies AI risk classification, recommends quarantine, creates tickets, and supports analyst review — without offensive phishing capabilities.
End-to-end workflow from source signals to human-approved action and audit logging.
01
Incoming Email
02
Email Analysis
03
Sender / Domain Analysis
04
URL / Attachment Indicators
05
AI Risk Classification
06
Risk Score
07
Quarantine / Flag Recommendation
08
Security Alert
09
Ticket / Notification
10
Analyst Review
Emails analyzed, suspicious/high-risk, quarantined, false positives, and resolved incidents (demo).
Sender, recipient, subject, timestamp, domain, risk score, severity, and status.
Demo indicators such as suspicious sender, domain mismatch, URL mismatch, attachment flags, urgency language, impersonation signals, and auth failures.
Detected → Under Review → Quarantined → Released → Confirmed Threat → False Positive → Resolved.
“Report Suspicious Email” submits metadata/demo sample for analysis, scoring, and ticketing.
Attempts over time, threat categories, impersonation patterns, high-risk domains, resolution rate.
Metrics and screens below are simulated for demonstration. Not live customer telemetry.
Integration capabilities with common security and IT systems — not claimed vendor partnerships.
Other portfolio demonstrations of customized security automation.
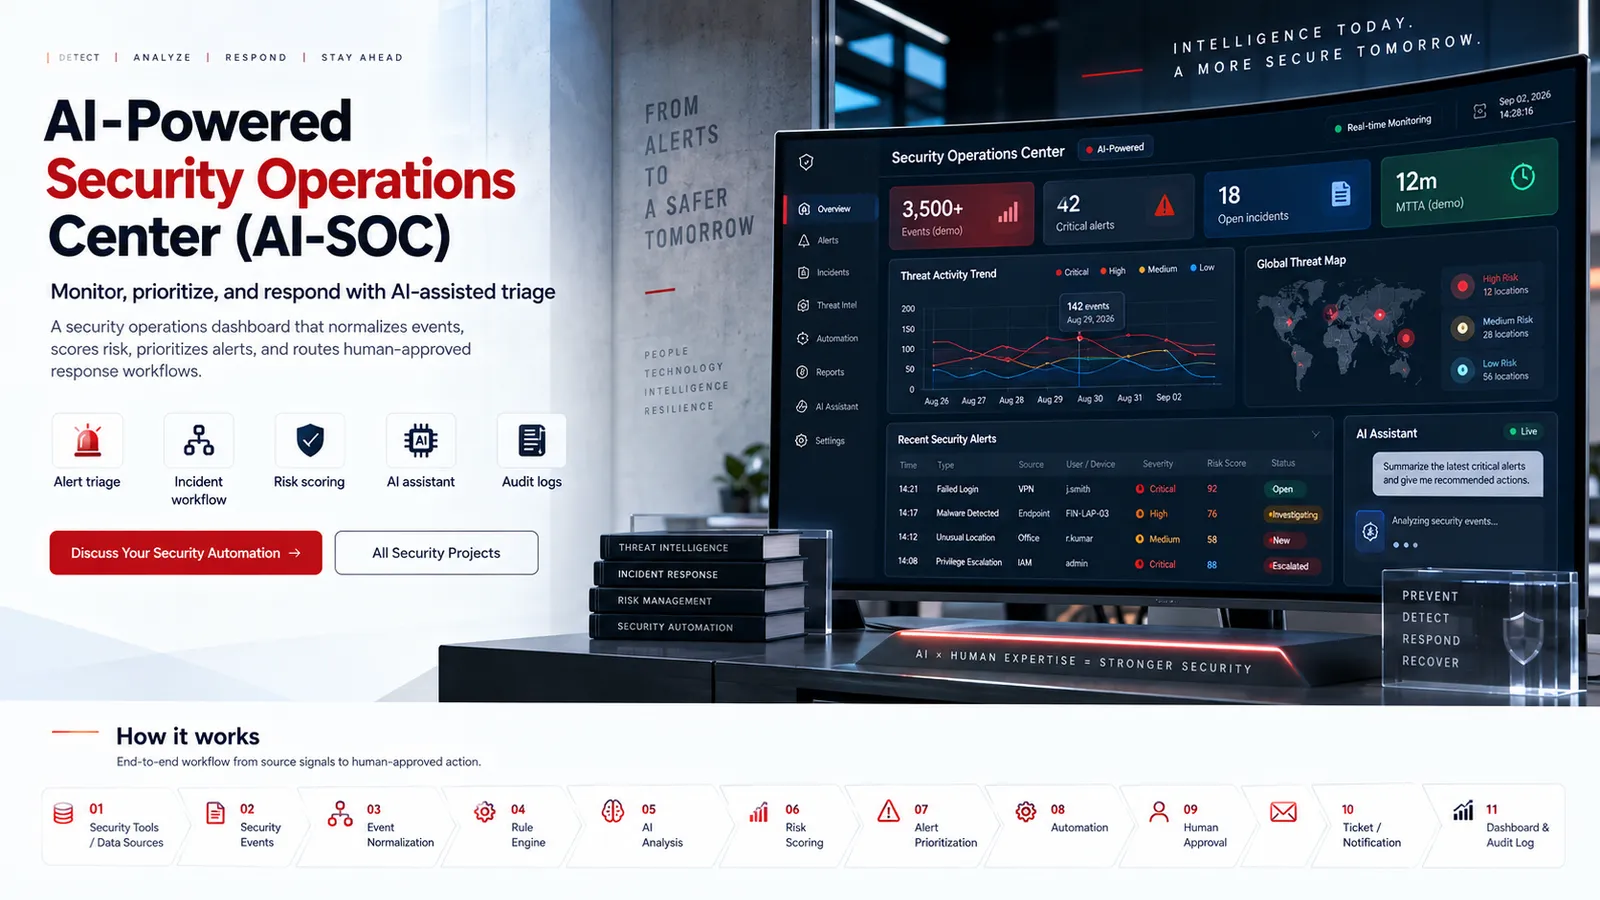 Security Operations
A security operations dashboard that normalizes events, scores risk, prioritizes alerts, and routes human-approved response workflows.
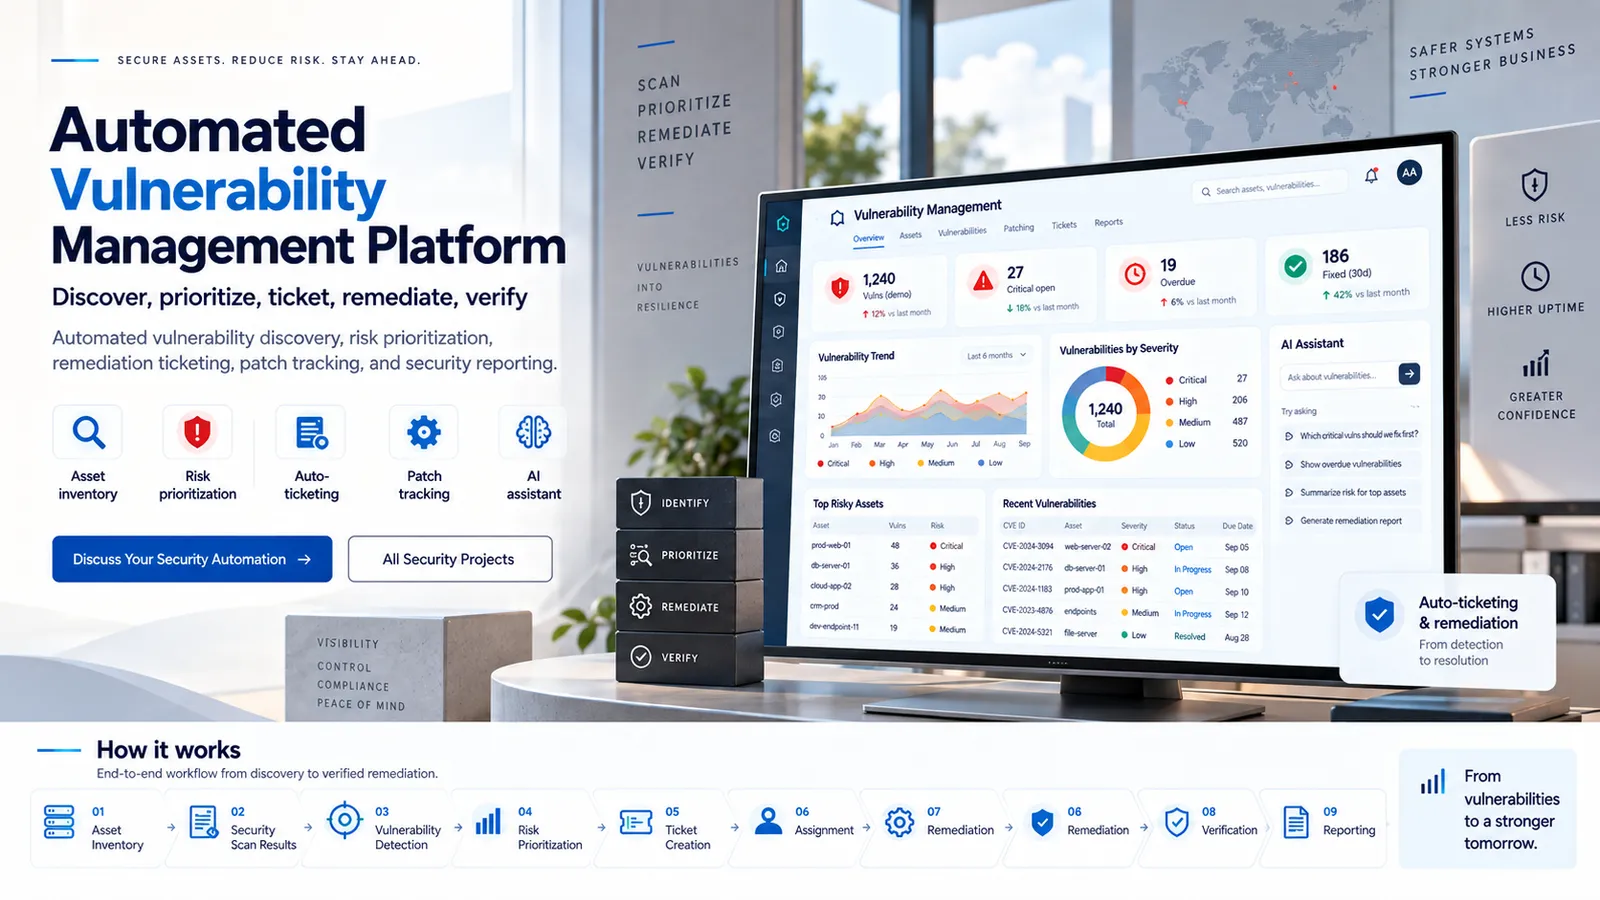 Vulnerability Management
Automated vulnerability discovery, risk prioritization, remediation ticketing, patch tracking, and security reporting.
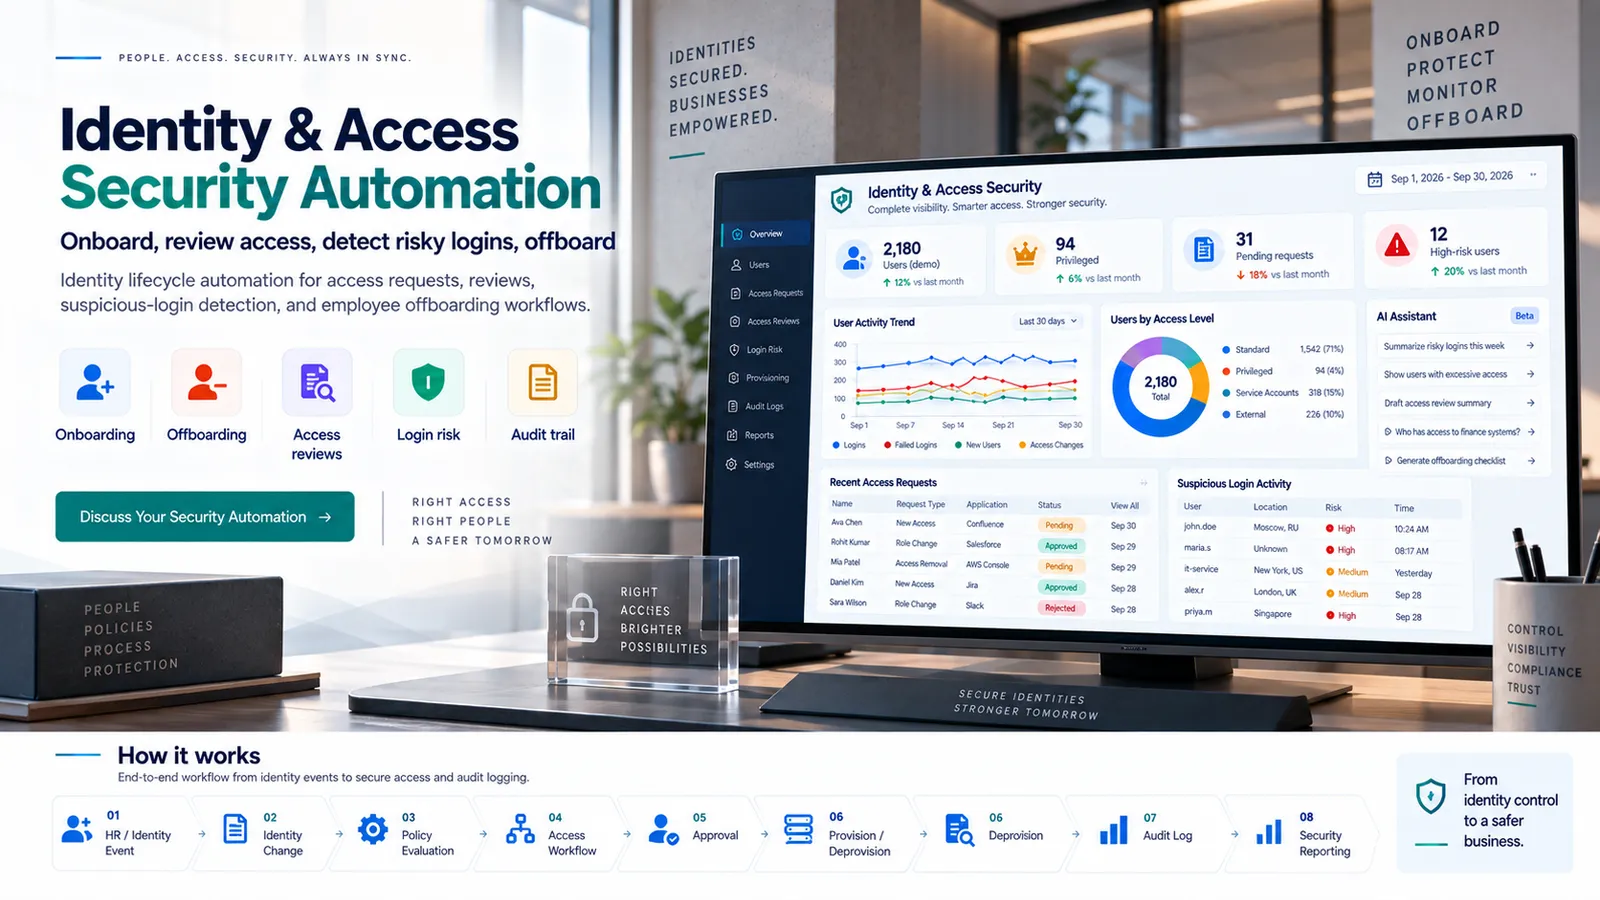 Identity Security
Identity lifecycle automation for access requests, reviews, suspicious-login detection, and employee offboarding workflows.
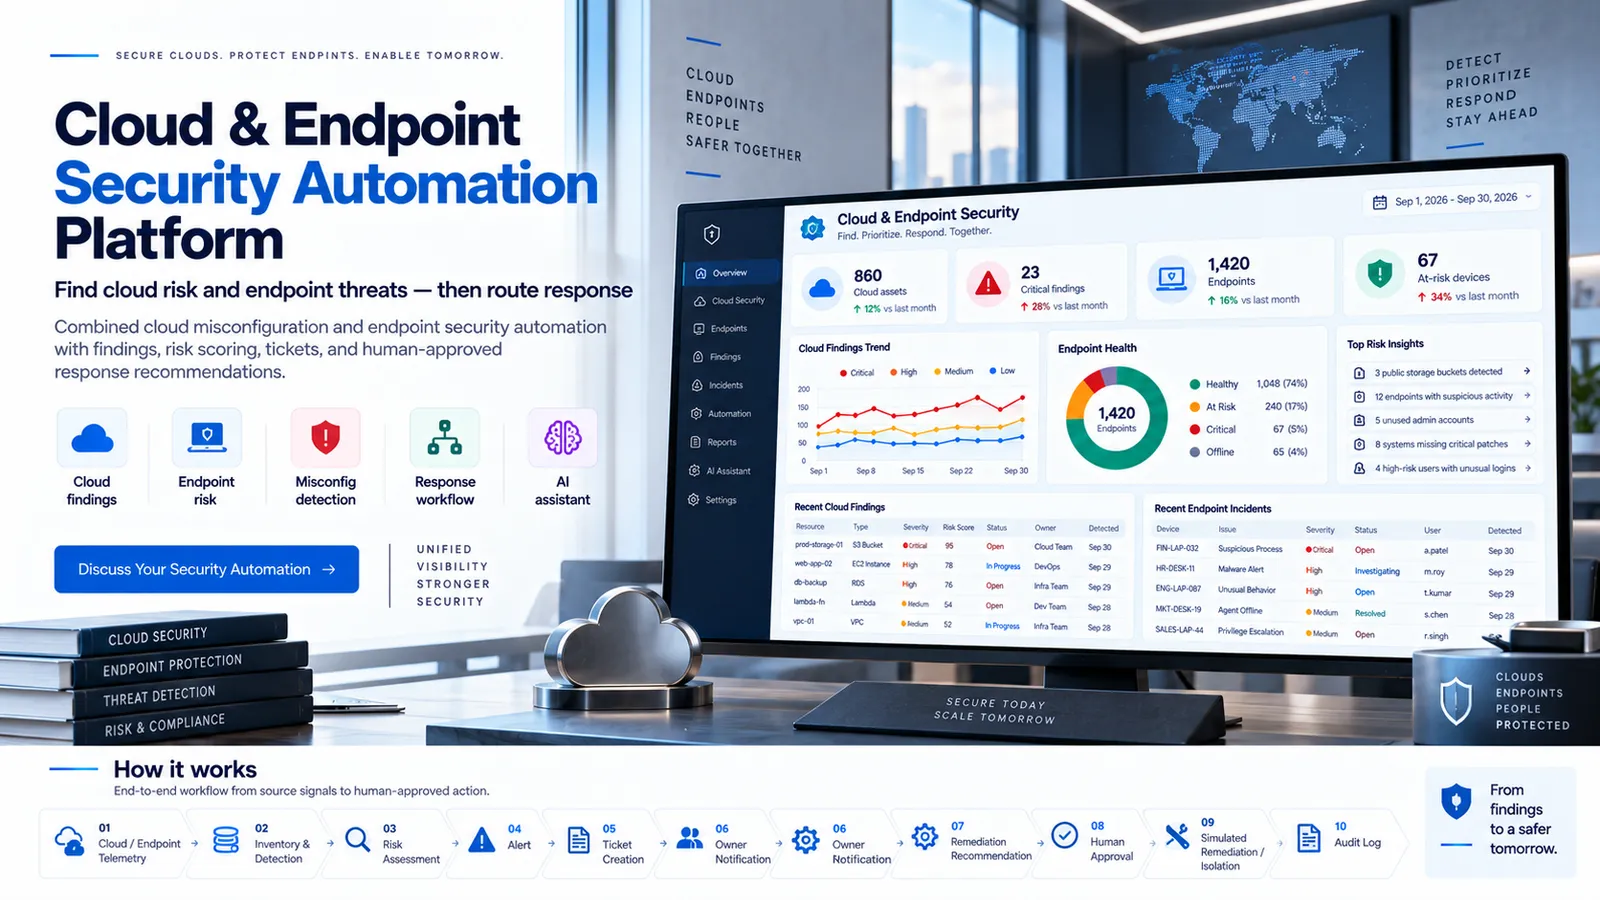 Cloud & Endpoint
Combined cloud misconfiguration and endpoint security automation with findings, risk scoring, tickets, and human-approved response recommendations.
Explore a custom security automation solution tailored to your tools and approval model.